IT Jargon
September 21, 2026 by Shawna Huskey
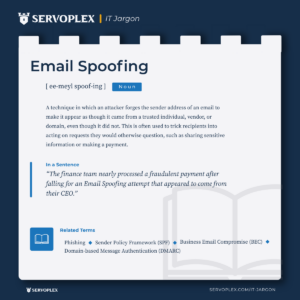
The Quick Explanation Simply Put: Email Spoofing is when an attacker forges the “from” address on an email to make it look like it’s coming from someone you trust, a coworker, a vendor, even your own company’s domain. The email itself never actually came from that person, but the display name and sender address are […]
Read more »
Tagged
September 14, 2026 / September 4, 2026 by Shawna Huskey
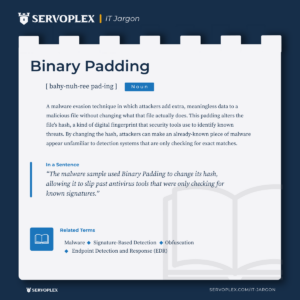
The Quick Explanation Simply Put: Binary Padding is a technique attackers use to disguise malware by adding extra, meaningless data to the file. This doesn’t change what the malicious program actually does, but it does change the file’s digital fingerprint, called a hash, which many security tools rely on to recognize known threats. Why it […]
September 7, 2026 / September 4, 2026 by Shawna Huskey
The Quick Explanation Simply Put: Prompt Injection is a technique where someone crafts specific input to manipulate an AI system, like a chatbot or AI assistant, into ignoring its intended instructions. Instead of using the tool the way it was designed to be used, the attacker gets it to do something else entirely, whether that’s […]
August 31, 2026 by Shawna Huskey
The Quick Explanation Simply Put: Fast Flux is a technique attackers use to rapidly change the IP addresses associated with a domain name. Instead of pointing a malicious website or server to one fixed location, they constantly rotate through different addresses. This makes phishing sites, malware infrastructure, and Command and Control (C2) servers much […]
August 24, 2026 by Shawna Huskey
The Quick Explanation Simply Put: HTML Smuggling is a technique where attackers hide malicious files inside what looks like an ordinary webpage or email attachment. Instead of sending the harmful file directly, they embed the pieces inside HTML or JavaScript code. Once the page loads in a browser, the browser itself puts those pieces back […]
865-245-9090