The Quick Explanation
Simply Put:
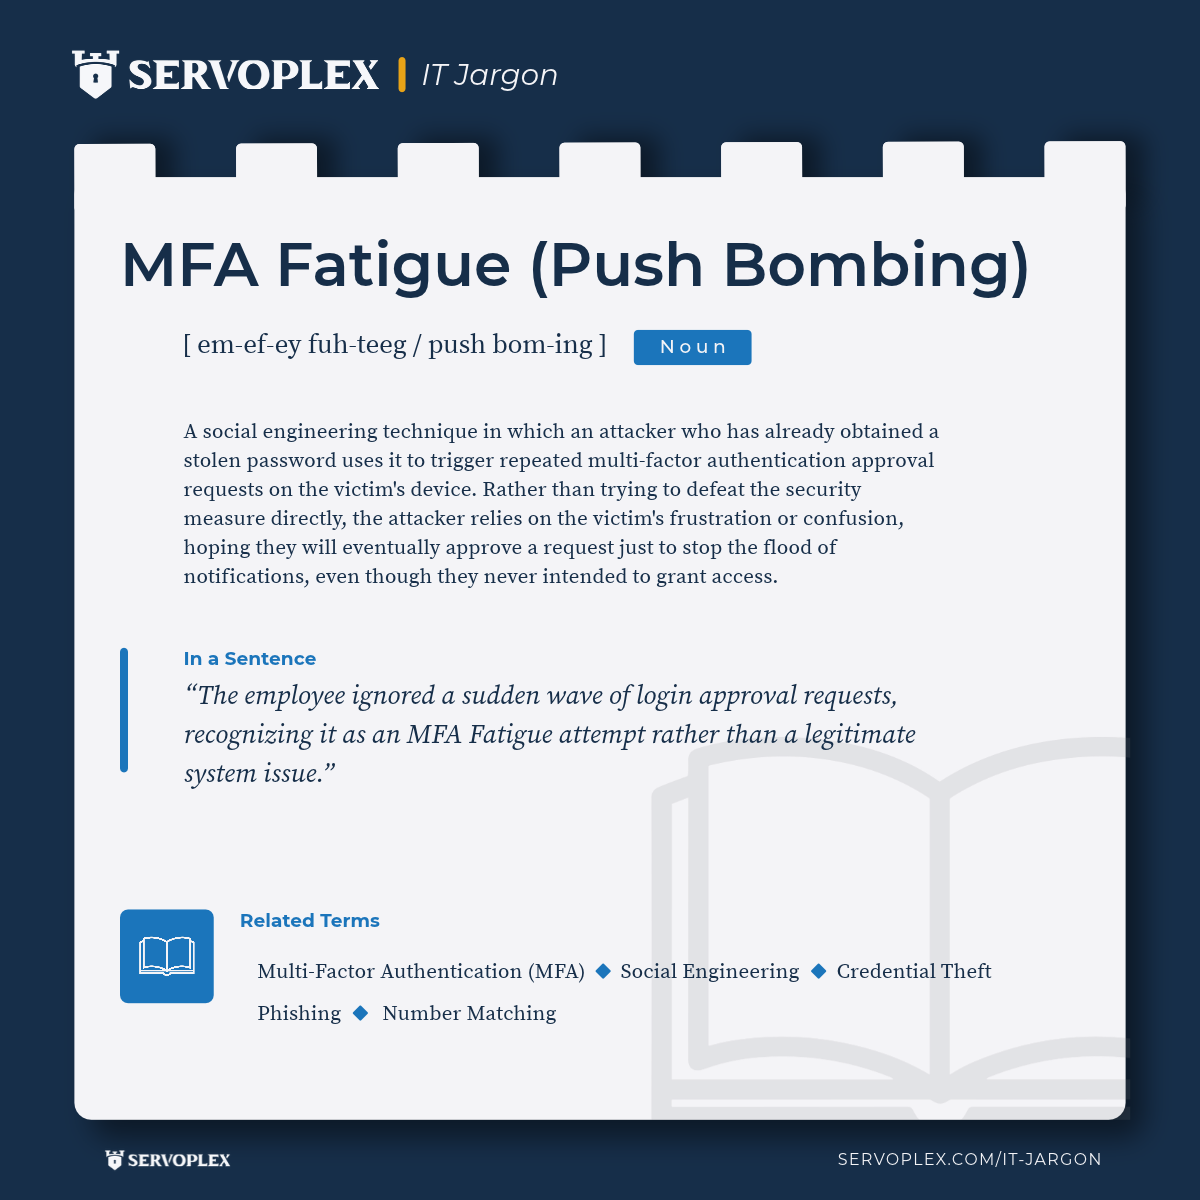
MFA Fatigue, also called Push Bombing, happens after an attacker already has a stolen password. Instead of stopping there, they use it to trigger a flood of multi-factor authentication approval requests on the victim’s phone, over and over, hoping the person eventually taps “approve” just to make the notifications stop.
Why it Matters:
Multi-factor authentication is one of the strongest defenses against stolen passwords, but this technique doesn’t try to break it, it tries to wear the person down. A single tap of frustration or confusion is all it takes to hand an attacker access, even when every other security layer worked exactly as intended.
This tactic has shown up in real, high-profile breaches, including incidents where attackers used stolen credentials paired with a wave of push notifications to get past MFA at major companies. It’s a reminder that MFA works best when people also know what a legitimate prompt should look like.
How We Protect Clients:
- Monitor client accounts around the clock for unusual authentication activity
- Configure MFA methods that require a code or number match instead of a simple approve or deny tap
- Educate employees to never approve an MFA request they didn’t personally trigger
- Set up alerts for repeated or unusual login attempts
- Include authentication practices in regular security reviews
See more…