The Quick Explanation
Simply Put:
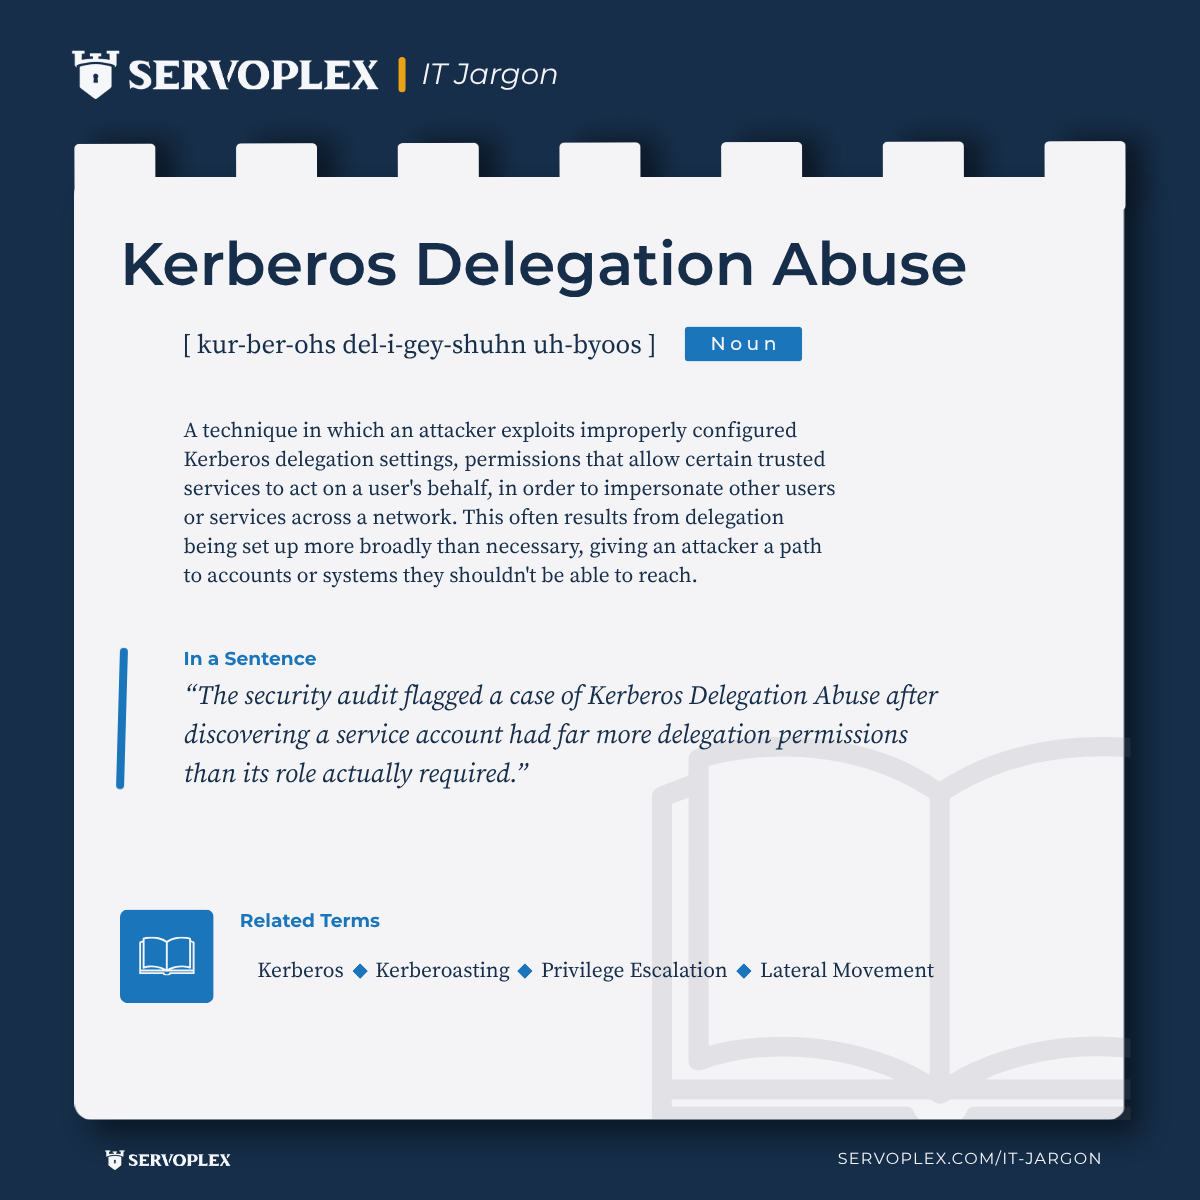
Kerberos Delegation Abuse happens when an attacker exploits misconfigured delegation settings in Kerberos, the authentication system many business networks use to verify identity. Delegation is meant to let certain trusted services act on a user’s behalf, but when it’s set up too loosely, an attacker who compromises one of those services can impersonate other users or services across the network, sometimes including highly privileged accounts.
Why it Matters:
This isn’t a flaw in Kerberos itself, it’s a flaw in how it’s configured. A single overly permissive delegation setting can quietly hand an attacker a path to impersonate accounts they were never supposed to have access to, often without triggering the kind of alarms a more obvious attack would.
How We Protect Clients:
- Monitor client networks around the clock for unusual authentication activity
- Review authentication and delegation configurations for overly broad permissions
- Limit which services and accounts are allowed to use delegation in the first place
- Apply the principle of least privilege across accounts and services
- Include identity and access configurations in regular security reviews
At ServoPlex, we know a permission that’s technically allowed isn’t the same as a permission that’s actually needed, and that gap is where attacks like this live.
See more…